Compliance
This page shows you which software is running on your connected gateways, and whether it contains any known vulnerabilities — as evidence for software bills of materials (SBOM) and for your own audits.
Checking your gateways' software state
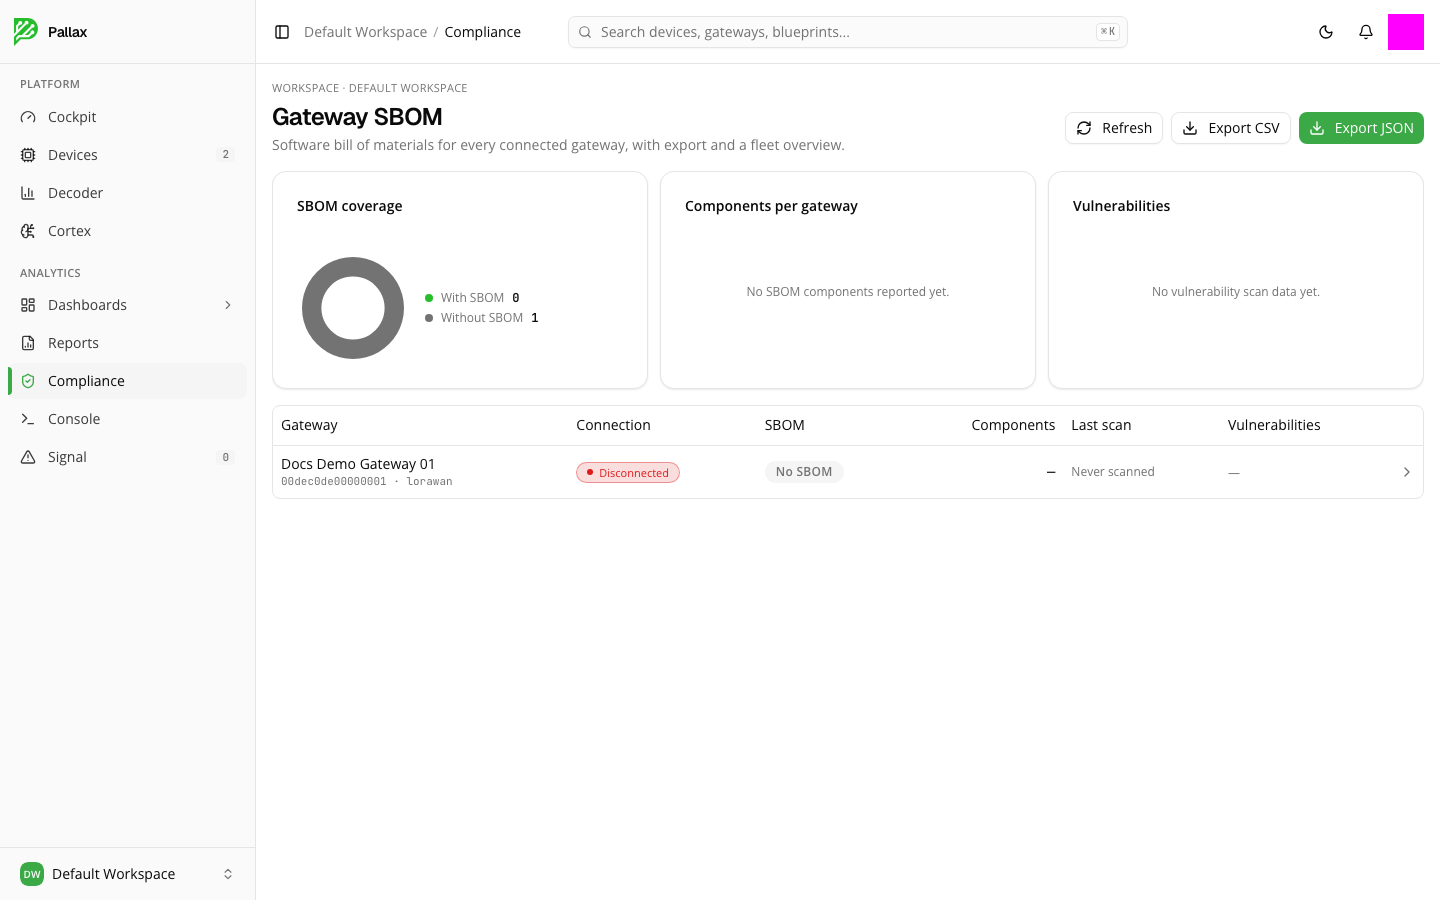
Three tiles summarize the state: SBOM coverage shows for how many of your gateways a software bill of materials is available, Components per gateway lists the software they contain, and Vulnerabilities shows security issues found. As long as no data is available yet, the page says so openly instead of showing placeholder values.
Below that, a table lists every gateway with its connection status, whether a software bill of materials is available, the number of components detected, the time of the last scan, and vulnerabilities found.
Refreshing and exporting data
Refresh reloads the table. Export CSV and Export JSON let you take the data with you for your own evidence or audits.